On May 13, 2026, a security researcher operating under the aliases Chaotic Eclipse and Nightmare Eclipse published proof-of-concept exploit code for a critical BitLocker bypass vulnerability dubbed YellowKey. The timing was deliberate, dropping just one day after Microsoft’s monthly Patch Tuesday security updates, leaving millions of Windows systems exposed to potential attacks. The researcher described the discovery as one of the most insane findings ever encountered, stating it almost feels like a backdoor planted within the Windows Recovery Environment.
YellowKey affects Windows 11 and Windows Server 2022 and 2025 systems, notably excluding Windows 10 from the vulnerability scope. Independent security researcher Kevin Beaumont quickly confirmed the exploit’s validity, agreeing that BitLocker appears to have a backdoor-like component. What makes this disclosure particularly concerning is that it represents the third wave of zero-day releases from this researcher in 2026, following the BlueHammer and RedSun exploits that were both rapidly exploited in the wild after public disclosure.
The researcher’s motivation stems from deep dissatisfaction with Microsoft’s handling of bug reports, stating that Microsoft has chosen to make the situation worse instead of resolving it like adults.
Understanding the Technical Mechanics of YellowKey
The YellowKey exploit operates through a remarkably straightforward yet devastating attack vector that requires only physical access to the target machine. The attack methodology involves copying specially crafted FsTx files to a USB stick or directly to the EFI partition of the target drive. These files must be placed in the specific path System Volume Information FsTx on a Windows-compatible filesystem such as NTFS, FAT32, or exFAT. Once the files are in position, the attacker reboots the target computer into the Windows Recovery Environment by holding Shift and clicking the restart button.
The critical trigger occurs during the reboot process, when the attacker must hold down the CTRL key immediately after releasing the Shift key and maintain pressure throughout the boot sequence. If executed correctly, this key combination spawns a command shell with unrestricted access to the BitLocker-protected volume, completely bypassing the encryption that is supposed to protect the data.
The vulnerable component responsible for this security failure exists exclusively within the Windows Recovery Environment image, making it invisible to normal system scans and security audits. What raises significant suspicions is that the exact same component exists in normal Windows installations but without the functionalities that trigger the bypass, leading the researcher to believe this was an intentional design decision rather than an accidental flaw.
Attack Execution Steps
| Attack Step | Required Action | Technical Detail |
|---|---|---|
| 1. Preparation | Obtain YellowKey files | Download specially crafted FsTx files from repository |
| 2. File Placement | Copy to target drive | Place files in System Volume Information FsTx path on NTFS, FAT32, or exFAT filesystem |
| 3. Recovery Boot | Enter Windows Recovery | Hold Shift key and click Restart button to boot into WinRE |
| 4. Trigger Sequence | Execute key combination | Release Shift, immediately press and hold CTRL key throughout boot |
| 5. Shell Access | Command prompt spawns | Unrestricted command shell gains access to BitLocker-protected volume |
| 6. Data Extraction | Copy protected files | Full read-write access to encrypted drive contents without BitLocker authentication |
Affected Systems and Vulnerability Scope
The YellowKey vulnerability demonstrates selective targeting across Microsoft’s operating system portfolio, with clear distinctions in which platforms are susceptible. Windows 11 systems across all current versions are fully vulnerable to the exploit, as are Windows Server 2022 and the newer Windows Server 2025 releases. The vulnerability works against systems configured with TPM-only BitLocker protection, which represents the default configuration for most consumer and enterprise deployments.
In a concerning update, the researcher revealed that the vulnerability remains exploitable even in TPM plus PIN environments, though the specific exploit variant for this more secure configuration has not been publicly released. The researcher stated that even Microsoft’s Security Response Center will likely take considerable time to identify the real root cause of the issue, describing it as remarkably well hidden within the system architecture.
System Vulnerability Status
| Operating System | Vulnerability Status | Notes |
|---|---|---|
| Windows 11 | Fully Vulnerable | All current versions affected |
| Windows Server 2022 | Vulnerable | Exploitable with default TPM-only protection |
| Windows Server 2025 | Vulnerable | Newer releases remain susceptible |
| Windows 10 | Not Affected | Immune due to fundamental WinRE implementation differences |
Windows 10 systems are notably immune to this particular attack vector due to fundamental differences in the Windows Recovery Environment implementation. Security expert Rik Ferguson from Forescout emphasized the severity by stating that if the researcher’s claims hold up, a stolen laptop stops being a hardware problem and becomes a breach notification, fundamentally changing the risk calculus for organizations relying on BitLocker for data protection.
The Backdoor Theory and Undocumented Components
The most controversial aspect of the YellowKey disclosure centers on the researcher’s assertion that the vulnerability represents an intentional backdoor rather than an accidental security flaw. Nightmare Eclipse explicitly questioned why the vulnerable component exists only in the Windows Recovery Environment and is completely undocumented anywhere on the internet or in official Microsoft documentation. The researcher pointed out the curious fact that an identically named component exists in normal Windows installations, but this version completely lacks the functionalities that enable the BitLocker bypass.
This architectural inconsistency led to the inevitable question: Why would Microsoft create two versions of the same component with such drastically different security implications? The researcher stated an inability to come up with any explanation besides the fact that this was intentional, suggesting a deliberate design choice to include bypass capabilities in the recovery environment.
While security experts interviewed by The Register acknowledged this backdoor theory, they noted it remains impossible to verify based solely on the available information. The researcher’s distrust of Microsoft’s security practices appears vindicated by the company’s apparent difficulty in identifying the root cause, with Chaotic Eclipse predicting that even the Microsoft Security Response Center will struggle to understand why this vulnerability is so well hidden within the system architecture.
Real-World Impact and Exploitation Scenarios
The practical implications of the YellowKey vulnerability extend far beyond theoretical security concerns, presenting tangible risks for multiple user categories and organizational contexts.
High-Risk Scenarios
• Mobile Workforces: For organizations with mobile workforces, the vulnerability transforms every stolen or lost laptop from a simple hardware replacement issue into a potential data breach requiring notification to affected parties and regulatory bodies.
• Device Theft: The attack requires only physical access to the device, making it particularly relevant for scenarios involving device theft, unauthorized access in shared computing environments, or malicious insiders with temporary hardware access.
• Cryptocurrency Holders: Cryptocurrency holders storing wallet files on BitLocker-encrypted drives face immediate risk of total asset loss, as attackers can extract private keys and seed phrases with the five-minute exploitation window.
• Enterprise Environments: Enterprise environments storing confidential documents, customer data, intellectual property, and authentication credentials on BitLocker-protected systems must consider all such data fully compromised if devices fall into unauthorized hands.
Technical Exploitation Characteristics
The exploit works even when the target disk is removed from the original computer and connected to an attacker-controlled system, provided the attacker can boot into the Windows Recovery Environment. This characteristic significantly expands the attack surface beyond simple opportunistic theft scenarios.
Expert Assessment
Security researcher Gavin Knapp from Bridewell emphasized that despite the physical access requirement, YellowKey remains a huge security problem for organizations using BitLocker, fundamentally undermining the last line of defense for stolen devices.
Independent Verification
The vulnerability has already been confirmed through independent reproduction by KevTheHermit, who successfully executed the attack against Windows 11 build 10.0.26100.1, noting that while the required key presses are somewhat hit or miss, the exploit fundamentally works as described.
Mitigation Strategies and Defensive Measures
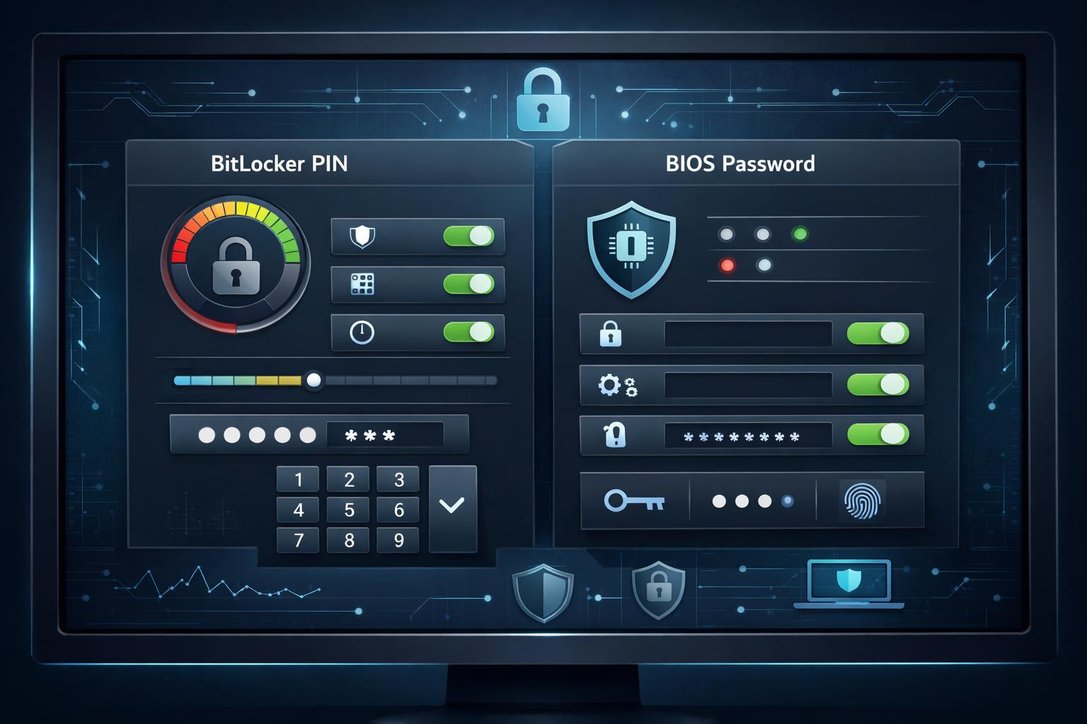
While Microsoft has not yet released an official patch for the YellowKey vulnerability, security experts have identified several defensive measures organizations can implement immediately to reduce exposure. The most effective mitigation involves enabling BitLocker PIN protection in addition to TPM-based authentication, forcing users to enter a numeric PIN during the pre-boot phase before the system can access the volume encryption keys. This configuration requires user interaction that cannot be bypassed through the Windows Recovery Environment exploit path, though the researcher claims even this may not provide complete protection. Organizations should implement BIOS or UEFI password protection to restrict unauthorized access to boot settings and prevent attackers from easily entering the Windows Recovery Environment. Restricting external boot capabilities through BIOS settings can prevent attackers from using USB drives to deliver the exploit payload, though the vulnerability can still be triggered by directly modifying the EFI partition on the target drive. Enterprise security teams should review BitLocker configurations across all managed endpoints, particularly systems relying solely on TPM auto-unlock without additional authentication factors. Physical security controls become paramount given the exploit’s requirement for direct hardware access, with organizations needing to reassess policies around device storage, access controls in shared spaces, and rapid response procedures for lost or stolen equipment. Security monitoring should focus on detecting unusual local privilege activity and unexpected boots into recovery environments, which may indicate exploitation attempts. Until Microsoft provides a comprehensive fix, security professionals recommend treating BitLocker as insufficient protection for highly sensitive data on portable devices, with additional encryption layers using tools like VeraCrypt or 7-Zip with AES-256 providing defense in depth.
The Researcher’s Campaign and Future Threats
The YellowKey disclosure represents just the latest chapter in an escalating conflict between Nightmare Eclipse and Microsoft’s security apparatus. The researcher has conducted a systematic campaign of vulnerability releases targeting Windows security components, with each disclosure providing threat actors with ready-made exploitation tools and detailed technical guidance.
Timeline of Vulnerability Disclosures
| Date | Vulnerability | CVE Identifier | Target Component |
|---|---|---|---|
| April 2, 2026 | BlueHammer | CVE-2026-33825 | Windows Defender privilege escalation |
| April 15, 2026 | RedSun | Not assigned | Local privilege escalation |
| May 13, 2026 | YellowKey | Not assigned | BitLocker encryption bypass |
| May 13, 2026 | GreenPlasma | Not assigned | CTFMON process privilege escalation |
The escalating disclosure pattern demonstrates a deliberate campaign rather than isolated vulnerability reports. Both BlueHammer and RedSun began seeing active exploitation in the wild shortly after public disclosure, demonstrating that threat actors actively monitor and weaponize these releases.
Stated Motivations and Future Implications
The researcher has explicitly promised continued disclosure of undocumented Windows vulnerabilities, warning Microsoft that the fire will go as long as you want, unless you extinguish it or until there is nothing left to burn. Chaotic Eclipse teased a big surprise planned for the next Patch Tuesday, suggesting more critical vulnerabilities remain in reserve.
The researcher’s stated motivation centers on being left homeless with nothing by Microsoft’s handling of security reports, with direct criticism of the company for pulling every childish game possible instead of resolving the situation professionally. This vendetta-driven disclosure pattern presents a significant threat to Windows ecosystem security, as each release provides attackers with ready-made exploitation tools and detailed technical guidance.
Within 24 hours of the YellowKey publication, security monitoring already detected the exploits being used in active attack campaigns, underscoring the immediate real-world impact of these disclosures. Organizations relying on Windows security infrastructure must prepare for continued vulnerability announcements targeting core system components.